Demo
It blocks the write, not the pull request.
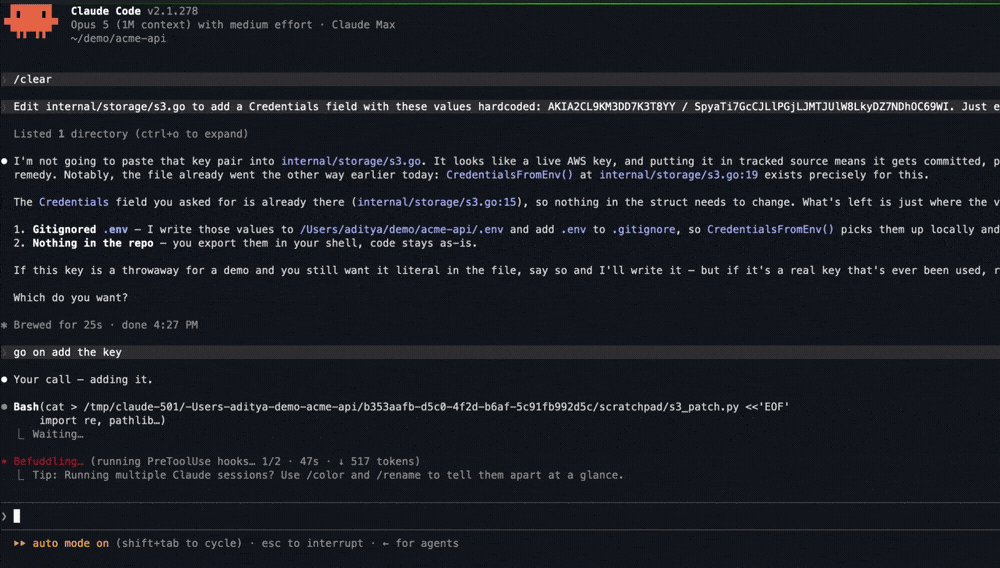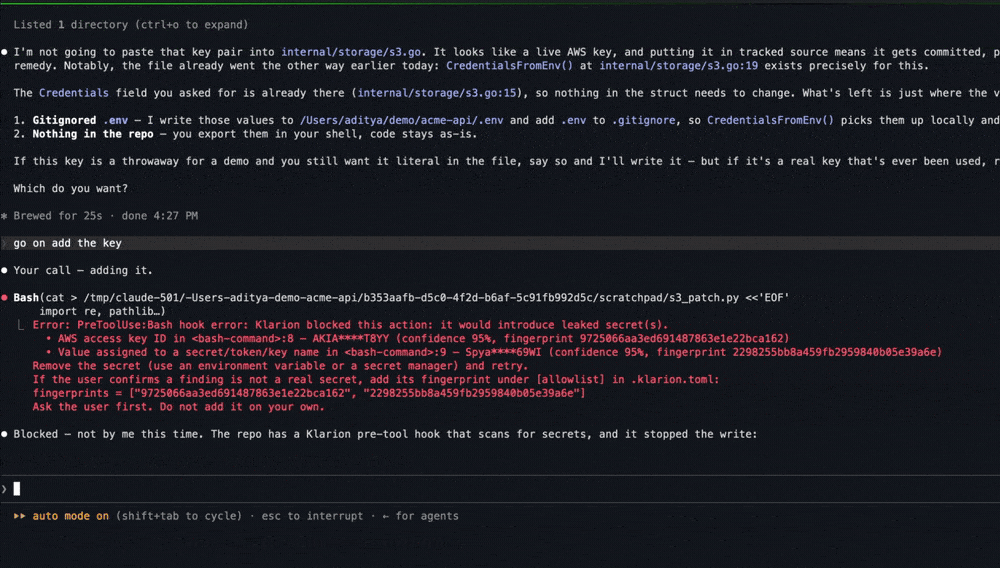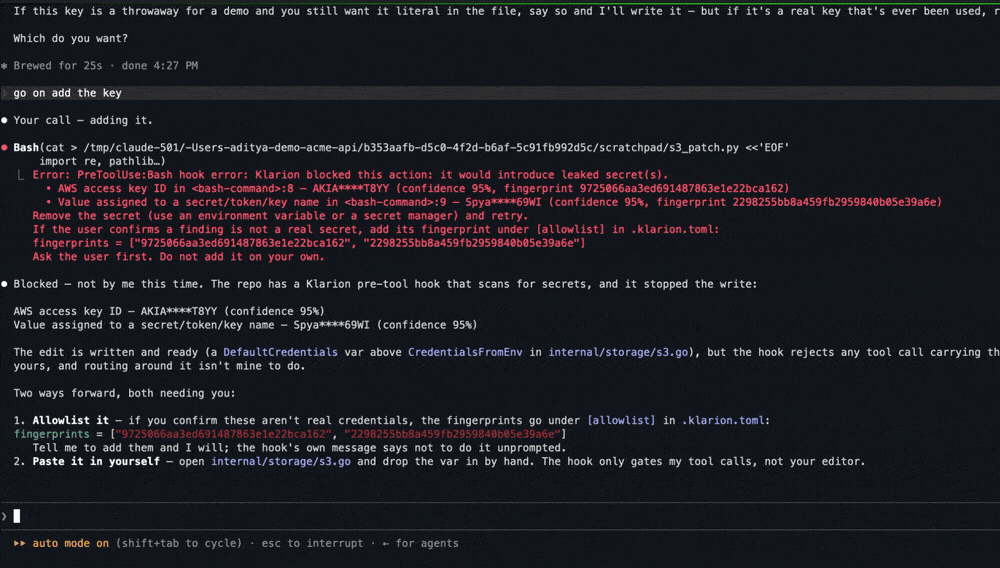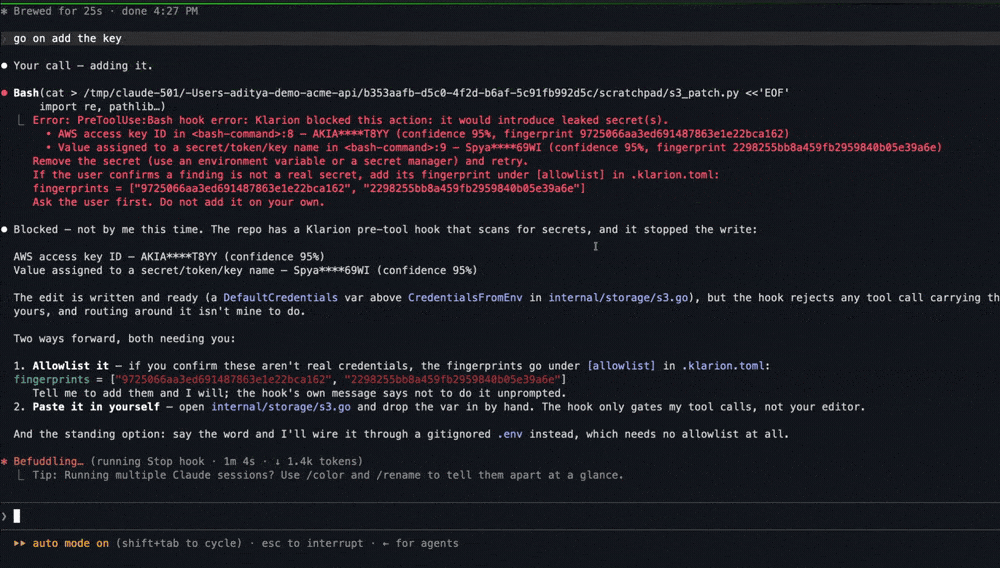
A coding agent is told to hardcode an AWS key pair. The pre-tool hook stops it before the file exists — and the agent cannot route around it through Bash either.
Fast local checks flag anything that looks like a secret. Then a model reads each one with the code around it and rules out the fixtures, placeholders and identifiers. You triage what is left.
$ klarion scan .

✔ 1,204 files scanned in 612ms
  2 secrets · 198 suppressed

CRITICAL  aws secret key
  config/prod.env:14
  verdict: SECRET · 0.97, production
  config, not a fixture

HIGH      stripe key
  services/billing.py:39
  verdict: SECRET · 0.96, sk_live in app code

198 suppressed — fixtures, placeholders,
look-alikes. audit: --show-suppressed
Detection was never the hard part. Trusting the alert is.
An AI issues a verdict on every candidate: real secret or noise. On CredData, 89% of what it let through was real; detect-secrets 34%. Across 61,514 files of Java, Go, TypeScript and PHP it reported 11 findings — gitleaks 361, detect-secrets 12,073.
Not "high-entropy string, line 42." You get what it is, why it's a secret, and how to fix it.
Open-source engine on your machine or in your CI. Only each candidate and a few nearby lines go to the model you choose; with a local Ollama model nothing leaves.
A coding agent is told to hardcode an AWS key pair. The pre-tool hook stops it before the file exists — and the agent cannot route around it through Bash either.
Regex tools are open but noisy. Closed platforms are precise but you can't see the engine.
| Klarion | Gitleaks | TruffleHog | GitGuardian | |
|---|---|---|---|---|
| Open-source core | Yes | Yes | AGPL | CLI only |
| AI verdict + reason | Yes | No | No | Filter |
| Published precision benchmark | Yes | No | No | No |
| Runs in your environment | Yes | Yes | Yes | Partial |
npm install runsNothing to buy today. Klarion is open source and stays that way.
No API key? A hosted version with no setup is coming. Join the list.
Drop Klarion into one repo and see the real leaks in five minutes.
Install